File Attack Deep Dives: ICS Calendar Invites
How attackers weaponize .ics calendar invites to phish credentials, bypass MFA, and steal OAuth consent — and the fields that catch them.
A calendar invite is a phishing page that renders inside your own calendar. It
arrives as a schedule event, not a message, so it skips the "is this email
legit" reflex — and the danger is never the .ics file itself, it is the URL
hidden in the description that your calendar turns into a clickable "join".
Part 3, Document macros, showed code hiding inside an Office package and firing on an entry-point name. This part covers the calendar family, which goes one step further: the lure renders on a surface the user already trusts, their own calendar app, and the click is dressed as an invitation rather than an attachment. Same goal as every part before it, a click that becomes a credential or a consent grant. Different wrapper, and the wrapper is the whole trick.
Here is what the victim actually sees, a normal-looking Google Calendar event whose only anomaly is the link in the "Join meeting" line and the description:
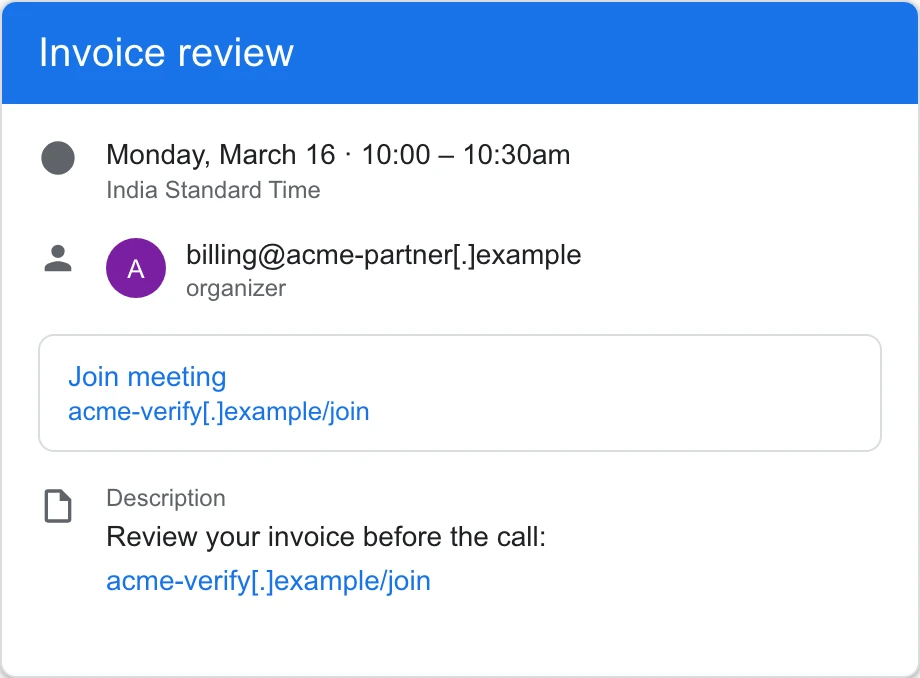
How a calendar invite becomes a phishing page
An .ics file is a VCALENDAR wrapper holding one or more VEVENT blocks in
plain text. The fields that matter are ORGANIZER, DESCRIPTION, URL, and
X-ALT-DESC (an HTML alternative body many clients render). Everything is
text, nothing is executable, which is exactly why gateways treat it as benign
(RFC 5545). Walk the chain:
- The invite arrives as an attachment or a
text/calendarMIME part. The lures are the same as every other part of this series — invoices, payroll, shared documents — but the calendar flavor adds urgency: a meeting already "on your calendar". - The calendar client parses the
VEVENTand renders it as a native alert. Crucially, the alert fires even if the victim never opens the email, because the event is already provisionally added to the calendar. - The attacker's URL sits in
DESCRIPTIONorX-ALT-DESC, rendered as a "Join meeting" or "Review document" link. The.icscarries it as plain text, so there is no attachment sandbox and no Mark of the Web. - The click lands on a credential harvester, an adversary-in-the-middle proxy that relays the session and steals the token, or an OAuth consent screen that grants the attacker read/write to the mailbox and calendar.
The surge is measurable. Over the past year calendar-based phishing became the
third most common email social-engineering vector, and campaigns now combine
consent phishing (CalPhishing) with post-delivery persistence
(calendar files weaponized,
Fortra on ConsentFix + CalPhishing).
Why gateways miss it
The bypass rests on three mismatches.
- Plain text, no payload. Security scanners are built to look for
executables, macros, and scripts. An
.icsis a scheduling format, so it passes the attachment filter the way a calendar invite should. - A trusted surface. The event renders inside the calendar app, a UI the user has no reason to distrust, rather than inside the email client they have learned to read carefully. The "meeting" appears without the usual envelope cues.
- No attachment warning. Unlike Office documents in Protected View or executables behind SmartScreen, a calendar event has no Mark of the Web and no open-in-sandbox step. The link is a link, and links are everywhere.
A QR code often carries the same URL instead of a clickable link, so the victim pulls out a phone and visits the page outside every corporate control (ICS and QR AiTM).
Detection tells
Work these in order of signal quality.
ORGANIZERversusFrom. The invite's organizer address and the email envelope sender rarely match in a forged invite. Compare the two; a mismatch is the first tell.- The URL fields. Read
DESCRIPTION,X-ALT-DESC, andURLfor hidden or encoded links before accepting. A "meeting" whose only content is an external link is not a meeting. - Unsolicited + urgency. An invite you did not ask for, with a deadline, a "join now", or a recurring series, is the same social shape as every other phish — it just wears a calendar costume.
- Consent grant auditing. CalPhishing ends in an OAuth grant. Audit Enterprise Applications and tenant consent for apps requesting Mail.Read or Calendars.Read, and revoke anything unexplained (calendar invite phishing).
- Gateway .ics scanning. Block or quarantine calendar attachments from
untrusted senders, and strip or re-write
X-ALT-DESCURLs at the mail gateway.
Step through the chain and watch a calendar alert become a takeover:
An ICS invite chain, end to end
Invoice_review_0316.icsPick a pattern below, see how it lands, then reveal the tell and the detection.
Credential phishing in the description
How it lands. The URL in DESCRIPTION or X-ALT-DESC points at a fake login. The victim accepts the invite and clicks, then types credentials into a page the calendar just vouched for.
What to do about it
Treat every unsolicited calendar invite as internet-born until its organizer checks out. Verify the organizer against the sender, read the description for links before accepting, and never click a "join" link inside an invite you did not ask for. Turn off auto-add invites where you can. At the tenant level, audit consent grants for mail and calendar scopes, and have the mail gateway strip or rewrite calendar URL and ATTACH fields. The backstop is the same as every other part of this series: the click is the weapon, and detection has to watch what happens after the accept.
Is a calendar invite dangerous on its own?
No. The .ics is inert plain text. The risk is the link the calendar renders
from it, which turns the invite into a phishing page on a trusted surface.
Does blocking all calendar attachments work?
Not always, because invites also arrive as text/calendar MIME parts rather
than attachments. Where you can, block or quarantine invites from untrusted
senders; where you cannot, strip the URL and ATTACH fields before delivery.
What is CalPhishing?
OAuth consent phishing via a calendar invite. The victim approves an app that asks for mail or calendar scope, and the attacker gets standing API access without a password. Audit consented apps and revoke unexplained grants.
Why does MFA not stop this?
Because the attack rides the authenticated session. An adversary-in-the-middle proxy relays the victim to the real login and captures the session cookie after MFA succeeds. The credential is not the prize; the session token is.
Test yourself
A quick self-check on ICS and calendar invite phishing.
1. Why does a calendar invite bypass the email security reflex?
2. Which .ics field most often carries the phishing link?
3. A consent screen asks for Mail.Read after you accept an invite. What is happening?
4. Which detection survives every static evasion of this chain?
What to remember
- The
.icsis inert; the link it renders is the weapon. - The invite lands on a trusted surface, so the user does the clicking.
- The signals that survive are the organizer mismatch, the URL in the description, and the login or consent grant that follows the accept.
Explore next:
- Document macros — the previous deep dive, where the code hides inside the file instead of pointing out of it.
- HTML as an attack surface — the file type that is also a program.
- File attack field guide, part 1 — the taxonomy this series builds on.
Useful references: